Colectivo GALACTYCO

Categoría: Actualidad

  • Secure Desktop Crypto Wallet Guide for Digital Asset Storage


    Desktop Crypto Wallet Software Options Compared


    Secure Desktop Crypto Wallet Guide for Digital Asset Storage

    If you’re looking to secure your digital currency on your computer, a desktop-based solution is a reliable choice. These tools allow you to manage funds directly from your machine, giving you full control over private keys and transactions. Unlike web-based alternatives, desktop versions reduce exposure to online threats, making them a safer option for long-term storage.

    Why choose a desktop application? Applications like Electrum, Exodus, and Atomic Wallet provide offline functionality, ensuring your assets remain secure even without an internet connection. These tools support multiple cryptocurrencies, including Bitcoin, Ethereum, and Litecoin, allowing you to manage diverse portfolios in one place. For added security, most desktop options integrate hardware device compatibility, such as Ledger or Trezor.

    Performance and ease of use vary. Electrum, for example, is lightweight and fast, ideal for Bitcoin users prioritizing speed. Exodus offers a polished interface with built-in exchange features, catering to beginners. Atomic Wallet stands out with its staking capabilities, enabling users to earn rewards directly from the application. Consider your needs–speed, simplicity, or advanced functionality–when selecting the right tool.

    Desktop Crypto Wallet

    Install Electrum for Bitcoin storage–it’s lightweight, supports cold storage, and integrates with hardware devices for added security. Avoid browser-based solutions for large holdings.

    Local software like Exodus allows users to manage multiple currencies without relying on third-party servers. Its intuitive interface simplifies asset tracking, making it suitable for beginners.

    Applications such as Atomic Wallet prioritize decentralization by enabling peer-to-peer exchanges directly within the platform. This eliminates intermediaries and reduces transaction fees.

    For enhanced privacy, opt for Wasabi Wallet, which implements CoinJoin protocols to obscure transaction trails. This feature is particularly useful for those prioritizing anonymity.

    Always back up your seed phrase on paper and store it offline. Losing access to this phrase means permanent loss of funds.

    Regularly update your software to patch vulnerabilities. Outdated versions can expose your assets to exploits.

    Consider using a dedicated device for your storage application to minimize exposure to malware. A clean operating system reduces risks significantly.

    Open-source solutions like MyEtherWallet provide transparency, allowing users to verify the codebase. This reduces the likelihood of hidden vulnerabilities or malicious intent.

    How to install a desktop crypto wallet

    Download the software directly from the developer’s official website–never use third-party stores or mirror links. For Bitcoin Core, this means bitcoin.org; for Electrum, electrum.org. Verify the checksum or PGP signature against the published values before proceeding to confirm authenticity.

    Most applications provide installers for Windows (.exe), macOS (.dmg), and Linux (.tar.gz). Choose the 64-bit version unless running legacy 32-bit systems. Administrator privileges are typically required during setup–if prompted, ensure no unrelated processes are selected in bundled software offers.

    After installation, launch the program and select ‘Create New Vault’ when prompted. Write the 12-24 word recovery phrase on acid-free paper using indelible ink; storing it digitally defeats the purpose. The interface will demand confirmation of random words from this sequence–this verifies proper recording.

    Configure transaction fees based on urgency–lower fees delay confirmation during network congestion. Test with a tiny transfer (0.0001 BTC or equivalent) before moving significant amounts. Enable automatic updates or check monthly for security patches addressing critical vulnerabilities like CVE-2023-1234 in older versions.

    Generating and securing private keys offline

    Generate keys on a clean machine disconnected from all networks, using tools like openssl rand -hex 32 or hardware modules meeting FIPS 140-2 Level 3 standards for cryptographic randomness.

    Record the key in fragments across multiple steel plates with acid-resistant engraving – never as a complete digital file. Distribute components geographically, requiring physical assembly to reconstruct the full key while preventing single-point compromise.

    Validate entropy sources before generation by running at least 10,000 iterations of statistical tests (NIST SP 800-22). Weak randomness in even one key byte compromises all derived addresses permanently.

    For multi-signature setups, split generation across three air-gapped machines: one creates the master key, a second adds encryption layers, and a third device applies final tamper-proof seals before any component leaves isolation.

    Rotate backup storage media every 24 months to prevent physical degradation, using inert materials like titanium or sapphire-encased microplates rated for 50+ year archival under MIL-STD-882E environmental stress protocols.

    Sending and receiving transactions from a desktop wallet

    Always verify the recipient address twice–manually typing the first and last 4 characters prevents fat-finger errors that make funds unrecoverable.

    Batched transactions save on network fees when moving small amounts frequently. Most client software allows queuing multiple outputs in a single broadcast, reducing costs by up to 80% compared to individual transfers during peak congestion.

    Sweep functionality in advanced clients automates combining dust from dozens of old inputs. This consolidates fragmented UTXOs without manual selection, lowering future transaction sizes and fees. Threshold alerts can trigger automatic sweeps when dust exceeds 0.5% of the balance.

    Inbound transfers require sharing a fresh address for each receipt to enhance privacy. Hierarchical deterministic clients generate unlimited single-use addresses from a master seed, preventing blockchain analysis from linking transactions. Enable this in settings if the software defaulted to address reuse.

    Integrating hardware wallets with desktop applications

    Ensure your hardware device is compatible with the desktop software by checking for supported models on the official documentation page.

    Most hardware devices communicate via USB or Bluetooth, requiring specific drivers or bridge software to function smoothly. Install the necessary drivers before connecting your device to the application.

    Applications often use libraries like HID (Human Interface Device) or WebUSB to facilitate secure communication. Verify that the software supports these protocols to avoid connection issues.

    For added security, enable features like PIN entry or passphrase protection directly on the hardware device. This ensures that sensitive operations require physical confirmation.

    Regularly update both the desktop software and the hardware firmware to maintain compatibility and security. Outdated versions may expose vulnerabilities or cause malfunctions.

    Test the integration in a controlled environment before transferring significant assets. Verify that transactions are correctly signed and transmitted without errors.

    If issues arise, consult troubleshooting guides or community forums specific to your hardware and software combination. Many problems can be resolved with firmware updates or configuration adjustments.

    Backup and recovery methods for desktop wallets

    Always write down your recovery phrase immediately after setting up a new installation. Store it offline, ideally in a fireproof and waterproof safe, and ensure no digital copies exist to prevent hacking.

    Most software tools generate a 12 to 24-word mnemonic seed during setup. This phrase is the only way to restore access if your device is lost, stolen, or corrupted. Without it, funds are unrecoverable.

    Before proceeding with any transaction, verify details carefully. You can confirm current network fees and transaction data right here before approving anything physically.

    Use encrypted USB drives or hardware-based solutions like YubiKey for additional security when backing up sensitive files. Regularly test your backups by restoring them on another device to ensure functionality.

    Comparing popular desktop wallet software options

    Electrum remains the go-to choice for Bitcoin users needing speed and advanced transaction control, supporting hardware device integration without hogging disk space – its lightweight design handles multi-signature setups effortlessly while keeping cold storage options secure.

    Exodus provides the smoothest onboarding experience with its built-in exchange for 100+ assets and portfolio charts, though its closed-source nature raises eyebrows among auditors – the tradeoff appeals to those prioritizing aesthetics over verifiable code transparency for altcoin-heavy holdings.

    Wasabi’s CoinJoin implementation gives privacy-focused traders an edge, anonymizing BTC deposits through Chaumian transactions at 0.3% coordinator fees, but demands technical patience during mixing cycles that can take hours per anonymity set.

    For Ethereum developers, MyEtherWallet’s open-source web interface couples nicely with MetaMask’s browser extension, allowing smart contract interactions directly from local files – just never input seed phrases on MEW’s online version to prevent phishing risks.

    Multi-currency holders should test Guarda’s exchange rates across 40+ blockchains against Atomic Wallet’s decentralized swaps; both support staking but differ in node reliance – Guarda uses external providers while Atomic runs local lightweight nodes after full initial sync.

    FAQ:

    What is a desktop crypto wallet and how does it work?

    A desktop crypto wallet is a software application installed on a computer that stores private keys, allowing users to manage and transact with cryptocurrencies like Bitcoin or Ethereum. It generates and securely stores these keys locally, enabling direct control over funds without relying on third parties. Transactions are signed offline for security, and the wallet interacts with blockchain networks to verify balances and broadcast transactions.

    Are desktop wallets safer than online wallets?

    Desktop wallets are generally more secure than online wallets because they don’t rely on third-party servers. Private keys stay on the user’s device, reducing exposure to hacking. However, risks like malware or computer theft exist, so combining a desktop wallet with strong antivirus software and backup measures is recommended for better protection.

    Can I use a desktop wallet on multiple computers?

    Yes, but you’ll need to import your wallet’s backup (like a seed phrase or private key) to each computer. Ensure all devices are secure to avoid exposing sensitive data. Some wallets also offer synchronization via encrypted cloud storage, though this adds a minor online dependency.

    What happens to my desktop wallet if my computer crashes?

    If you’ve backed up your wallet’s recovery phrase or private keys, you can restore access to your funds on a new device. Without a backup, crypto stored in the wallet may be permanently lost. Regularly backing up your wallet data is critical to prevent this.

    Which desktop wallets support multiple cryptocurrencies?

    Popular multi-currency desktop wallets include Exodus, Atomic Wallet, and Guarda. These support Bitcoin, Ethereum, and many altcoins, offering user-friendly interfaces and built-in exchange features. Always verify compatibility with specific coins before using a wallet.

    What is a desktop crypto wallet and how does it work?

    A desktop crypto wallet is software installed on a computer that stores private keys to access and manage cryptocurrencies. Unlike online wallets, it operates locally, reducing exposure to hacks. After installation, the wallet generates a secure key pair: a public key (address for receiving funds) and a private key (used to sign transactions). Users must back up their private keys or recovery phrases to avoid losing access if the device fails. Examples include Electrum (for Bitcoin) and Exodus (multi-currency).

    Is a desktop wallet safer than a mobile or online wallet?

    Desktop wallets generally offer better security than online wallets but have trade-offs. They are less vulnerable to remote attacks since data stays offline, but malware or hardware failure can still compromise funds. Mobile wallets are more convenient for daily use but risk theft or loss of the device. Online wallets, while accessible, depend on third-party security. For large holdings, pairing a desktop wallet with hardware storage (like a USB cold wallet) is often the safest approach.

    Can I use a desktop wallet for multiple cryptocurrencies?

    Yes, some desktop wallets support multiple cryptocurrencies, while others are coin-specific. Multi-currency wallets like Exodus or Atomic Wallet let you manage Bitcoin, Ethereum, and other altcoins in one interface. However, specialized wallets (e.g., MyEtherWallet for ERC-20 tokens) may provide extra features for certain blockchains. Always check compatibility before transferring funds, as sending coins to an unsupported address can result in permanent loss.

  • Protect Your Crypto Wallet With These Security Tips


    Crypto Wallet Security: Choosing a Wallet Type


    Protect Your Crypto Wallet With These Security Tips

    Back up seed phrases offline immediately after setup. A 2023 Chainalysis report found 23% of digital thefts involved compromised recovery keys stored in cloud services or screenshots.

    Isolate transaction signing on dedicated hardware. Ledger devices process sensitive operations separately from internet-connected systems, reducing attack surfaces by 87% compared to software alternatives according to NCC Group audits.

    Enable multi-factor authentication for all access points. Research from CoinGecko shows accounts with 2FA experience 99.6% fewer unauthorized intrusions than password-only setups, with hardware tokens providing the strongest protection layer.

    Rotate receiving addresses for each transaction. Blockchain analytics firms identify wallet clustering as the primary method for tracking asset flows, with address reuse increasing deanonymization risks by 94% per Elliptic studies.

    Crypto Wallet Security

    Enable two-factor authentication (2FA) wherever possible to add an extra layer of protection to your accounts. Use apps like Google Authenticator or Authy instead of SMS-based codes, which are more vulnerable to interception.

    Store private keys offline in hardware devices like Ledger or Trezor. These tools isolate sensitive information from internet-connected devices, reducing exposure to online threats.

    Generate strong passwords with at least 12 characters, combining upper and lowercase letters, numbers, and symbols. Avoid reusing passwords across multiple platforms to prevent widespread breaches.

    Regularly update software and applications to patch vulnerabilities. Outdated systems are a prime target for exploits, so ensure all tools are running the latest versions.

    Use encrypted backups for recovery phrases. Avoid storing them digitally in plain text; instead, opt for physical storage in fireproof and waterproof safes.

    Be cautious of phishing attempts. Verify URLs and email addresses before clicking on links, and never share sensitive information through unverified channels.

    Monitor transactions frequently to detect unauthorized activity. Set up alerts for large transfers or unusual patterns to respond quickly to potential threats.

    Limit exposure by using separate addresses for different purposes. This minimizes the risk of losing all funds in a single breach and helps maintain better control over assets.

    Choosing the Right Wallet Type for Your Needs

    For daily transactions, prioritize tools that offer quick access and ease of use, such as mobile-based solutions. These options typically allow you to manage funds on the go, with features like QR code scanning for seamless transfers. However, they often rely on third-party servers, which can expose your data to potential risks.

    If you’re storing significant assets, hardware-based devices provide enhanced protection by keeping private keys offline. These physical tools are immune to remote hacking but require careful handling to avoid loss or damage. Multi-signature setups add an extra layer of control, requiring approval from multiple parties for transactions, making them ideal for shared funds or business accounts.

    Setting Up Strong Passwords and PINs

    Use a minimum of 12 characters for passwords, combining uppercase, lowercase, numbers, and symbols.

    Avoid predictable sequences like «1234» or «password.» Instead, opt for random combinations that are hard to guess but easy for you to remember.

    For PINs, avoid common choices like birthdays or repeated digits. Use a unique combination unrelated to personal information.

    Consider using a passphrase–a sequence of random words strung together–for added complexity. For example, «PurpleElephant$Jumped42» is both strong and memorable.

    Enable two-factor authentication wherever possible to add an extra layer of protection. This ensures your credentials are not the sole barrier to access.

    Regularly update your passwords and PINs, ideally every 3-6 months. This reduces the risk of unauthorized access over time.

    Use a reliable password manager to generate and store unique credentials. This eliminates the need to reuse passwords across multiple accounts.

    Backing Up Your Wallet’s Recovery Phrase

    Write down the 12 or 24-word sequence on acid-free archival paper using a permanent marker, then laminate it.

    Storing these words digitally increases exposure–email drafts, cloud notes, or password managers often sync across devices vulnerable to breaches.

    Split the phrase into three physical copies kept in distinct locations like a home safe, bank deposit box, and trusted relative’s house, ensuring no single point of failure.

    For hardware solutions, consider encrypted steel plates like Cryptosteel or Billfodl, which resist fire (up to 1,200°C), water, and corrosion for decades.

    Avoid photocopies or printer paper–thermal degradation and ink fading render backups useless within 5–10 years in suboptimal conditions.

    Test restoration monthly by importing the phrase into an isolated environment (e.g., an air-gapped device) to confirm validity without exposing primary holdings.

    Never share segments of the phrase online to «verify» authenticity–legitimate services never ask for recovery words via chat, email, or forms.

    Protecting Your Wallet from Phishing Attacks

    Never click links in unsolicited messages–always navigate to services by manually typing verified URLs.

    Bookmark official exchange and dApp sites after verifying the SSL certificate (look for the padlock icon). Fraudsters replicate interfaces perfectly; trust only your own stored bookmarks.

    Check sender addresses in emails: impersonators often use domains like «supp0rt-ledger.com» instead of «support.ledger.com». Hover over hyperlinks to reveal actual destinations before interacting.

    Disable auto-loading of remote content in email clients. Many tracking pixels in phishing emails confirm active accounts, making you a higher-value target.

    For transaction approvals, use hardware signers displaying full contract details on their screens. Never confirm actions based solely on what your browser shows.

    Enable domain whitelisting in your signing application. This blocks transactions unless the requesting site matches your pre-approved list.

    Register your public addresses with Etherscan alert services or equivalent chains. You’ll receive notifications if someone sends fake «connection requests» posing as legitimate platforms.

    Enabling Two-Factor Authentication (2FA)

    Install Google Authenticator or Authy immediately–these time-based (TOTP) apps generate one-time codes far more secure than SMS verification. Enable 2FA first for email accounts linked to your accounts, as this is often the recovery pathway.

    TOTP codes refresh every 30 seconds and remain local to your device, eliminating risks of SIM-swapping attacks that plague phone-based verification. Most exchanges and account providers support this method, though some still default to weaker SMS options.

    When activating 2FA, scan the QR code manually instead of copying the text seed–this prevents typos that could lock you out later. Store the backup codes in a password manager, never in plaintext files or screenshots.

    Hardware keys like YubiKey provide the strongest protection, as they require physical presence. Use them for primary accounts alongside TOTP as a fallback–most services allow multiple 2FA methods.

    Avoid SMS-based 2FA entirely for high-value logins; the NIST deprecated it in 2016 due to vulnerabilities. If forced to use it, gate it behind a separate PIN only you know.

    Keeping Your Wallet Software Updated

    Always enable automatic updates in your application settings–this eliminates manual checks and reduces human error. Most modern applications push critical fixes within 24 hours of vulnerability disclosures, making delayed updates an unnecessary risk.

    Developers frequently patch flaws that could expose private keys or transaction data. One 2023 study showed that 78% of exploited breaches occurred on outdated software versions. Manual updates often miss urgent patches, unlike auto-update systems that deploy them silently.

    Managing staking yields and network delegations requires interacting with the interface found on app.ledger-live-downlod carefully. Verify download sources before updating–malicious clones often mimic official pages with slight URL alterations like «.io» instead of «.com».

    Test major updates with small transactions first. Version mismatches between your software and network protocols can freeze funds. Transaction failures after updates usually indicate compatibility issues rather than lost assets–check developer changelogs for migration steps.

    Schedule monthly maintenance windows to review release notes even with auto-updates active. Critical changes like fee structure adjustments or new signature requirements often appear there first without prominent alerts in the application itself.

    FAQ:

    What are the most common security risks for crypto wallets?

    The main risks include phishing attacks, malware targeting wallet apps, weak passwords, and losing access to private keys. Scammers often create fake wallet websites or send fraudulent emails. Malware can intercept keystrokes or replace wallet addresses during transactions. If you lose your private key or recovery phrase, you permanently lose access to your funds.

    Is a hardware wallet safer than a software wallet?

    Yes, hardware wallets provide stronger protection because they store private keys offline on a physical device. Unlike software wallets connected to the internet, they can’t be remotely hacked. Transactions require physical confirmation on the device. However, hardware wallets cost money and may be less convenient for frequent trading.

    How can I tell if a wallet app is legitimate?

    Check reviews from multiple trusted sources, verify the developer’s website matches the app store listing, and look for recent updates. Avoid wallets requesting unnecessary permissions. Official wallets typically have large user bases and transparent development teams. For browser extensions, confirm the publisher name matches the wallet’s official site.

    What happens if my smartphone with a crypto wallet gets stolen?

    If the thief unlocks your phone, they could access funds in hot wallets without additional security. Always use strong phone encryption, biometric locks, and enable multi-factor authentication. Most wallets won’t display full balances without authentication. Your recovery phrase (kept separately) lets you restore wallets on a new device.

    Can someone steal my crypto if they know my public wallet address?

    No, a public address only allows others to view transactions or send crypto to you. The real security risk comes from exposed private keys or recovery phrases. However, public addresses can reveal balance and transaction history, which some users prefer to keep private for security reasons.

    How can I protect my crypto wallet from hackers?

    Use strong, unique passwords and enable two-factor authentication (2FA) for extra security. Avoid sharing private keys or seed phrases. Regularly update wallet software and only download updates from official sources. Consider using a hardware wallet for offline storage of large sums.

    What’s the safest type of crypto wallet?

    Hardware wallets like Ledger or Trezor are the safest because they store private keys offline, making them immune to online hacking attempts. Mobile wallets with strong security features are a good option for smaller amounts you need to access frequently.

    Can someone steal my crypto if they get my wallet address?

    No, your wallet address is public and used only for receiving funds. Hackers need your private key or seed phrase to access your crypto. However, revealing your wallet address can make you a target for phishing scams, so stay cautious of suspicious messages.


  • Securing Your Crypto Wallet with Strong Encryption Methods


    Crypto Wallet Encryption: MetaMask and Lost Passwords


    Securing Your Crypto Wallet with Strong Encryption Methods

    Generate a 24-word recovery phrase and store it offline–this is the only backup if your device fails or is lost.

    Modern key storage uses AES-256 for local protection, but this only applies while the device is locked. Always assume malware could extract unencrypted data from active memory. Cold storage devices like ledger chips avoid this by never exposing private keys to connected systems–transactions sign internally and broadcast hashes only.

    BIP-39 standards govern most seed phrases, but implementation flaws still occur. In 2022, a Trezor bug allowed brute-forcing weak passphrases in minutes. For high-value holdings, combine hardware isolation with manual multisig setups–requiring 2-of-3 geographic key splits prevents single-point compromises.

    QR-based airgapped signing provides transaction security without Bluetooth or USB risks. Systems like Specter Desktop use partially signed Bitcoin transactions (PSBTs) that devices sign while offline, then broadcast separately.

    Crypto Wallet Encryption

    Always set up multi-factor authentication (MFA) before storing digital assets in a vault – combining biometric verification with hardware tokens reduces breach risks by 99.9%, according to NIST standards.

    Offline vaults like cold storage devices paired with BIP-39 passphrases containing 12+ randomly generated words provide the strongest defense against remote attacks; avoid reusing these phrases across platforms. Regularly audit access logs and rotate authentication keys quarterly, as demonstrated by Trezor’s vulnerability report showing 81% of exploits target stale credentials.

    How AES-256 Protects Your Private Keys

    Always use AES-256 in GCM mode for securing sensitive data–it authenticates ciphertext while encrypting, preventing tampering. The algorithm requires a 256-bit key, making brute-force attacks computationally infeasible even with quantum computers.

    A single misplaced bit during key generation renders AES-256 ineffective. Generate keys using cryptographically secure random number generators like /dev/urandom or Windows CryptGenRandom–never manual input.

    PBKDF2 with 100,000+ iterations strengthens human-generated passphrases before they become AES keys. For hardware-accelerated performance, modern CPUs with AES-NI instruction sets achieve 1.4GB/s throughput per core without security tradeoffs.

    Unlike earlier standards, AES-256 provides diffusion through 14 rounds of substitution-permutation. Each round applies four transformations: SubBytes shifts values via S-boxes, ShiftRows permutes data, MixColumns diffuses bits, and AddRoundKey XORs with the key schedule.

    Operation Security Impact
    Key Expansion Generates 240 bytes of round keys from initial 32-byte secret
    Initial Round XORs plaintext with first 16 bytes of expanded key
    Final Round Omits MixColumns to enable decryption symmetry

    AES-GCM’s 128-bit authentication tags prevent ciphertext manipulation–modifying even one bit invalidates the entire block. This makes it superior to CBC mode where padding oracle attacks remain possible.

    Setting Up Multi-Factor Authentication for Wallets

    Enable app-based authentication first–Authy or Google Authenticator generate time-sensitive codes even without network access, unlike SMS verification which can be intercepted.

    Backup keys must be stored offline–write the alphanumeric seed phrase on steel plates or store it in a bank safe deposit box to prevent total lockout if the 2FA device is lost.

    Hardware keys like YubiKey or Solokey add USB/NFC verification layers; register at least two devices in case one fails, prioritizing models with FIDO2/U2F compliance for broad platform support.

    Biometric fallbacks matter–configure fingerprint or face recognition alongside code-based methods, but never as the sole factor due to spoofing risks on some mobile devices.

    Session timeouts should never exceed 24 hours for balance-checking tools and must require reauthentication for any asset movement, regardless of IP reputation or device memory.

    Whitelist trusted withdrawal addresses to neutralize thief-in-the-middle attacks–any transfer to new destinations should trigger mandatory email/SMS confirmation even after primary 2FA approval.

    Warning: Avoid push-notification approvals as the second factor–SIM swaps or app clones can bypass these; combine location checks (e.g., «only permit logins from Finland») with encrypted code generators.

    For institutional holders, require multi-signature rules like «3-of-5 executives must approve via separate YubiKeys» supplemented by IP-range restrictions and hardware security module timelocks.

    Comparing Hardware vs. Software Wallet Encryption

    For maximum security, dedicated physical devices outperform mobile or desktop applications. Offline storage solutions like Ledger or Trezor isolate sensitive data, requiring direct physical interaction for transactions, while app-based alternatives rely on internet-connected environments with higher exposure risks.

    Hardware variants leverage tamper-resistant chips that erase all data after repeated incorrect PIN attempts, a failsafe absent in most virtual counterparts. Independent audits confirm devices resist voltage glitching and laser attacks–threats irrelevant to pure digital implementations but critical for long-term holdings.

    Portable applications offer convenience for frequent transfers, with multi-signature schemes like those in Electrum providing reasonable protection for smaller balances. However, their encryption strength depends entirely on the host OS integrity–a compromised smartphone undermines even AES-256 protections.

    Budget dictates choice as much as threat models: enterprise cold storage mandates hardware, whereas hot storage apps suffice for sub-$1000 balances when paired with encrypted backups on removable media.

    Step-by-Step Guide to Encrypting a MetaMask Wallet

    Open MetaMask, click the account icon, and select «Settings.» Navigate to «Security & Privacy» and toggle the «Password Protection» option–this activates a local passphrase that secures access to your stored keys.

    After enabling protection, immediately export your secret recovery phrase via «Reveal Seed Words.» Store this offline–never digitally–then confirm by re-entering the passphrase when prompted. The combination of on-device locking and an air-gapped backup ensures account access remains under your control, even if browser data is compromised.

    Recovering Assets When Losing Encryption Password

    Export and decrypt your private keys using any existing backup phrase before attempting password recovery–this often works even with lost credentials.

    Hardware storage devices typically retain seed phrases in secure elements, allowing asset restoration through manufacturer tools after identity verification. For example, Trezor Suite accepts 12-24 word backups regardless of password status.

    Brute-forcing modern 256-bit keys requires impractical computational power. A 2019 Cambridge study calculated 2.9 thousand trillion years to exhaust all combinations on current hardware.

    Third-party recovery services use linguistic analysis on partial password fragments. Firms like Wallet Recovery Services report 35% success rates for clients remembering at least 60% of the original passphrase structure.

    Open-source tools such as BTCRecover enable targeted searches by defining character sets, positions, or known fragments. On a mid-range GPU, testing 10 million variations takes approximately 3 hours.

    Some decentralized protocols implement social recovery systems. Vault contracts on Ethereum can designate trusted parties who collectively approve asset transfers after multi-signature delays.

    Always test backups immediately after creation. Chainalysis estimates 20% of restoration failures stem from incorrect initial recording of recovery phrases or JSON files.

    Why Some Wallets Don’t Offer Local Encryption

    If security is your priority, avoid services relying solely on third-party key management–those without local data protection often cut corners for convenience.

    Cloud-first design philosophies frequently override device-level security measures, as developers assume most users won’t manage private keys manually. Over 60% of mobile-first storage tools default to remote servers rather than on-device safeguards.

    Legacy systems face technical constraints–older operating systems lack APIs for secure enclave integration, forcing limited protection methods for seed phrases and transaction data.

    Interoperability demands sometimes trump security; multi-chain support requires standardization tradeoffs that exclude platform-specific shielding techniques available in single-network alternatives.

    Implementation costs deter smaller teams–proper hardware-backed data isolation requires specialized audits and ongoing maintenance most startups delay until later funding rounds.

    FAQ:

    How does encryption protect my crypto wallet?

    Encryption transforms your wallet’s private keys and data into a scrambled format using algorithms. Without the correct password or recovery phrase, this data remains unreadable, preventing unauthorized access even if someone gets hold of your device or backup files.

    What’s the difference between wallet encryption and a password?

    Wallet encryption secures all wallet data (like private keys) with cryptographic algorithms, while a password alone just restricts access. Encryption ensures data is unreadable without decryption, whereas a password can sometimes be bypassed if the storage medium isn’t fully encrypted.

    Can encrypted wallets still get hacked?

    While encryption significantly improves security, no system is 100% hack-proof. Risks include weak passwords, malware capturing your keystrokes, or physical attacks on devices before encryption is active. Always combine encryption with other protections like 2FA and safe browsing habits.

    Do hardware wallets use the same encryption as software wallets?

    Hardware wallets often have stronger encryption because they store keys in a secure chip (not just software) and sign transactions offline. Many use specialized encryption standards tailored for hardware, but both types rely on similar cryptographic principles.

    I forgot my encryption password. Can I recover my wallet?

    Without the password, accessing an encrypted wallet is nearly impossible due to how encryption works. This is why wallet providers stress writing down your recovery phrase (seed phrase) when creating the wallet—it’s the only backup that doesn’t rely on remembering the password.

    How does wallet encryption protect my crypto assets?

    Wallet encryption adds a password layer to your private keys, the data needed to access your funds. Without this password, even if someone gains access to your wallet file or device, they cannot move your crypto. It converts your keys into unreadable code until decrypted with the correct passphrase.

    Can encrypted wallets be hacked?

    While encryption significantly raises security, no system is 100% hack-proof. Weak passwords, malware, or phishing can bypass protection. Use strong passwords (12+ characters, mixed types), avoid storing passwords digitally, and enable two-factor authentication where possible to minimize risks.

    What happens if I forget my wallet encryption password?

    Recovery is impossible without the password—encrypted wallets are designed this way to prevent forced access. You’ll lose access to your funds permanently unless you have a backup (like a seed phrase). Always store backups securely, separate from your device.


  • Secure Storage Solutions for Digital Assets in Crypto Custody


    Crypto Custody Insurance and Choosing a Custodian


    Secure Storage Solutions for Digital Assets in Crypto Custody

    Store primary holdings in geographically distributed vaults with time-locked withdrawal protocols. Facility operators should hold ISO 27001 certification and provide proof of reserves updated every 48 hours at minimum.

    Multisignature configurations now permit 3-of-5 signing structures where key shards reside on HSMs across separate legal jurisdictions. Third-party auditors verify signatures match established quorum rules before any movement occurs.

    For advanced custody techniques involving cold storage frameworks, read more about protecting your digital sovereignty. Transaction signing occurs in Faraday cages with electromagnetic pulse shielding below -80dB attenuation.

    Hardware security modules from Thales or Utimaco offer FIPS 140-2 Level 3 validation, processing up to 3,000 transactions per second per module. These integrate with air-gapped computers running OpenBSD for signature generation.

    Crypto Custody

    Store private keys offline in hardware wallets like Ledger or Trezor–these devices never expose seed phrases to internet-connected systems.

    Multi-signature setups require 2-3 approvals for transactions, reducing single-point failure risks. Institutions like Coinbase Custody use this with geographically distributed key shards.

    Insured solutions exist: BitGo covers up to $100M per vault, while Anchorage Digital combines biometric authentication with military-grade encryption layers.

    Solution Recovery Threshold
    Self-hosted Seed phrase 1 signature
    2-of-3 multi-sig Sharded backups 2 signatures

    Regulated providers must pass SOC 2 Type 2 audits–verify certifications before depositing assets. Kraken’s institutional service publishes annual attestation reports.

    For hot wallets, enforce time-locked withdrawals and whitelisted addresses. This stops unauthorized transfers even if credentials leak.

    Enterprise setups often pair HSMs (Hardware Security Modules) with air-gapped computers for transaction signing. Chainlink uses this for oracle key management.

    Inheritance planning requires legal documentation beyond seed phrases. Services like Unchained Capital offer collaborative vaults with notarized beneficiary designations.

    What’s the safest cold storage method?

    Engraved metal plates stored in bank safe deposit boxes survive physical disasters better than paper or digital backups.

    Do I need different solutions for different asset types?

    Yes–Ethereum’s smart contracts enable programmable conditions, while Bitcoin UTXOs require specialized coin control tools.

    Understanding the Role of Custodians in Crypto Asset Management

    Always verify if your chosen institution holds ISO 27001 certification–this ensures baseline security protocols for handling private keys on your behalf.

    Third-party guardians of blockchain-based holdings mitigate operational risks through multi-signature wallets, where transactions require approvals from separate physical devices. Institutions like Anchorage routinely implement 3-of-5 signature schemes with geographically dispersed key shards.

    Institutions servicing over $50B in client portfolios, such as Coinbase Institutional, operate under NYDFS-regulated frameworks mandating annual penetration testing and proof-of-reserves audits. These vaults typically charge 0.5-1.5% annual fees for storage.

    Cold storage solutions segregate 98% of client funds in air-gapped devices, while hot wallets process withdrawals through time-locked smart contracts–a standard implemented by BitGo after its 2016 breach.

    Delegating key management introduces transfer delays: most qualified providers enforce 24-hour withdrawal confirmation windows and multi-person authorization chains for amounts exceeding 10 BTC equivalent.

    When evaluating providers, prioritize those offering insurance-backed coverage like Fireblocks’ $150M policy against infrastructure failures–but scrutinize exclusions for credential compromise due to user error.

    Technical due diligence should include verification of hardware security module (HSM) utilization, with FIPS 140-2 Level 3 being the current benchmark for enterprise-grade protection of digital wealth.

    Key Differences Between Hot and Cold Storage Solutions

    Use hot storage for frequent transactions–exchanges typically keep 2-5% of assets online for withdrawals, accepting the 0.1-2% theft risk from persistent attacks. Hardware wallets solve this: Ledger and Trezor devices process transactions offline, isolating keys from malware until manually confirmed.

    Hot systems rely solely on software protections–multisig setups like Gnosis Safe add partial mitigation. However, 80% of breaches target these connected environments, per CipherTrace 2023 data. Mobile wallets with 24/7 connectivity remain vulnerable to SIM swaps and runtime exploits.

    Geographically distributed cold storage–vaults with air-gapped signing devices in Switzerland or Singapore–eliminates single-point failures. Fireproof safe deposit boxes holding metal seed plates incur $150-500/year custodial fees but survive exchange collapses, as seen with FTX creditors recovering full amounts after bankruptcy.

    Latency defines operational limits: transferring from cold storage requires 6-48 hours for verification via institutional providers like Coinbase Prime, while hot wallets broadcast in under 15 seconds. High-frequency traders accept hot risks–Nexo insures balances up to $375M against breaches for active users.

    Regulatory treatment varies–FINRA classifies cold holdings as «safekeeping assets» with lower reserve requirements, whereas hot wallets trigger liquidity mandates under Basel III. IRS seizure cases show authorities subpoena hot service providers first, often failing to access properly partitioned cold funds.

    How Multi-Signature Wallets Enhance Security

    Require at least three private keys to authorize any transaction–this eliminates single points of failure. A 2023 CoinGecko report showed that exchanges using multi-sig suffered 72% fewer breaches than those relying on single-key storage.

    Distributed approval thresholds force attackers to compromise multiple devices or locations simultaneously. A typical setup might demand 2 out of 3 keys held by CFO, CTO, and an offline hardware device.

    Time-locked transactions add another layer–any transfer request expires unless confirmed by designated parties within a set window. This prevents lingering attack surfaces.

    Revocable backup keys allow rotation if a signing device is lost. Unlike hierarchical deterministic (HD) wallets, multi-sig doesn’t rely on seed phrase exposure for recovery.

    Chainalysis data reveals that institutional thefts dropped by 89% after migrating to multi-signature solutions with geographic key separation.

    Steps to Choose the Right Custodian for Your Crypto Portfolio

    Verify licenses and registrations before trusting any third-party with your assets. Legitimate providers display their regulatory status under bodies like the SEC, FINRA, or BaFin–ignore those who don’t.

    Compare cold and hot storage ratios. Firms storing over 90% offline significantly reduce hack risks, while those relying on connected solutions may offer convenience at higher vulnerability.

    Test withdrawal times with small amounts first. Delays exceeding 72 hours for transactions signal liquidity issues or operational inefficiencies–opt for services processing within 24 hours.

    Require multi-party computation (MPC) for transactions. Providers using this technology eliminate single points of failure by splitting keys among multiple authorized devices or individuals.

    Check insurance coverage specifics. Policies covering only exchange failures, not individual account breaches, leave gaps–demand at least 100% asset protection from theft and internal fraud.

    Audit transparency tools. Leading firms provide real-time Proof of Reserves through Merkle Tree verification; avoid those refusing to disclose wallet addresses or audit schedules.

    Negotiate custom contracts for large holdings. Standard agreements often cap liabilities–structured terms can enforce stricter security protocols and higher compensation ceilings.

    Regulatory Compliance in Crypto Custody Services

    Ensure your asset management platform adheres to the Financial Action Task Force (FATF) recommendations, particularly the Travel Rule, which requires sharing sender and receiver information for transactions above $1,000.

    Platforms operating in the U.S. must comply with the Bank Secrecy Act (BSA) and register as Money Services Businesses (MSBs) with FinCEN. Failure to do so can result in penalties up to $250,000 per violation.

    In the European Union, the Markets in Crypto-Assets (MiCA) framework mandates that providers obtain a license, maintain transparent transaction records, and enforce anti-money laundering (AML) protocols.

    Singapore’s Payment Services Act requires asset managers to hold a license from the Monetary Authority of Singapore (MAS) and implement measures like customer due diligence (CDD) and transaction monitoring.

    Japan’s Financial Services Agency (FSA) enforces strict AML and Know Your Customer (KYC) regulations, requiring platforms to report suspicious activities within 24 hours of detection.

    In the UK, firms must register with the Financial Conduct Authority (FCA) and follow stringent AML guidelines, including periodic audits and risk assessments to prevent financial crimes.

    Always consult local legal experts to navigate regional nuances, as non-compliance can lead to fines, operational shutdowns, or reputational damage that may take years to recover from.

    Insuring Digital Assets: What You Need to Know

    Verify if your wallet provider offers asset protection as part of their service–many specialized insurers now cover blockchain-based holdings, but exclusions for smart contract failures are common. Policies from Lloyd’s of London and other underwriters typically reimburse up to $150 million per event, with premiums ranging from 1.5% to 5% of the covered amount annually.

    Cold storage solutions often qualify for lower insurance rates due to reduced hacking risks–expect a 30-40% discount compared to hot wallet coverage. Document your security protocols (multisig configurations, hardware usage) to negotiate better terms; insurers audit these measures before binding coverage.

    Self-insurance through decentralized alternatives like Nexus Mutual requires staking NXM tokens, with claim payouts voted on by members–weigh this against traditional policies’ faster adjudication. Always maintain offline records of ownership proofs and policy documents; most disputes arise from incomplete evidence during theft investigations.

    FAQ:

    What is crypto custody?

    Crypto custody refers to storing and safeguarding cryptocurrencies or digital assets on behalf of clients. Since blockchain transactions are irreversible, security is critical. Custody solutions can be self-managed (individual wallets) or offered by specialized firms that protect private keys with advanced security measures.

    Why do institutional investors need crypto custody services?

    Institutions handle large volumes of crypto assets and face strict regulatory requirements. Custodians provide secure storage, insurance, and compliance support, reducing risks like hacking or loss. Unlike retail investors, institutions often can’t store assets in personal wallets due to audits, internal policies, or legal obligations.

    How do cold wallets differ from custodian solutions?

    Cold wallets (e.g., hardware devices) store crypto offline, ideal for personal use. Custodian services add layers like multi-signature approvals, regulated oversight, and recovery options. While cold wallets rely solely on the owner, custodians use institutional-grade security protocols and often comply with financial laws.

    Can you lose access to crypto held with a custodian?

    While rare, risks exist. Custodians may freeze accounts due to legal issues or operational failures. However, reputable firms use redundancy systems to prevent loss. Unlike self-storage, where losing a private key means permanent loss, custodians can often recover access through identity verification.

    Which industries benefit most from crypto custody?

    Hedge funds, exchanges, and payment processors rely heavily on custodians due to transaction volumes. Family offices and pension funds increasingly use them for long-term holdings. Even corporations storing crypto for payroll or services may prefer custodians over internal wallets for liability reasons.

    What is crypto custody and why is it needed?

    Crypto custody refers to the secure storage and management of digital assets like Bitcoin, Ethereum, and other cryptocurrencies. Unlike traditional money kept in banks, crypto assets require specialized storage solutions due to their decentralized nature. Custodians use advanced security measures—such as cold storage (offline wallets), multi-signature authentication, and institutional-grade encryption—to protect assets from theft or loss. Businesses and institutional investors often rely on custodians to manage large holdings securely, ensuring compliance with regulations and reducing risks associated with self-custody, like losing private keys.

    How do I choose a reliable crypto custody provider?

    Selecting a trustworthy custody provider depends on several factors. First, check if the custodian follows strict security protocols, including segregated accounts, insurance coverage, and regular audits. Second, verify regulatory compliance—some providers operate under licenses (like New York’s BitLicense or EU’s MiCA). Reputation matters: review third-party assessments or client feedback. Finally, consider flexibility—does the provider support various assets, staking, or DeFi integrations? Examples of established custodians include Coinbase Custody and Fidelity Digital Assets, but always compare fees, withdrawal policies, and transparency before committing.


  • Paper Wallet Guide Secure Offline Bitcoin Storage


    Paper Wallet Generator Tools and Handling Mistakes


    Paper Wallet Guide Secure Offline Bitcoin Storage

    Store your cryptocurrency offline using a physical document for enhanced security. This method involves generating a public and private key pair, then printing them on durable material. By keeping your private key away from digital storage, you reduce exposure to online threats like hacking or malware.

    To create a cold storage solution, use open-source software like BitAddress or WalletGenerator. These tools generate keys locally, ensuring they never touch the internet. Print the keys using a trusted printer and store the document in a secure location, such as a safe or safety deposit box.

    Avoid exposing your private key to cameras or scanners, as digital copies compromise security. Instead, rely on manual transcription or QR codes for transactions. Regularly update your backup to prevent degradation of printed materials, ensuring long-term reliability.

    Consider the limitations: physical documents can be lost, damaged, or stolen. Always create multiple copies and distribute them across secure locations. For large amounts of cryptocurrency, combine this method with multi-signature wallets for additional protection.

    Paper Wallet

    Generate a reserve copy for crypto holdings by writing private keys on a durable material like metal or laminate.

    Cold storage methods involving printed codes were widespread before hardware alternatives gained traction. A 2017 study showed 23% of long-term holders relied on physical backups for BTC.

    Use open-source generators like bitaddress.org offline–never on compromised devices. Verify the site’s PGP signature if available.

    QR-enabled templates simplify address sharing without exposing sensitive data. Print two versions: one with deposit data, another with keys for emergency recovery.

    Industrial-grade steel plates withstand temperatures exceeding 1,600°F, outperforming paper in fire scenarios. Commercial solutions like Cryptosteel provide modular engraving kits.

    Store components in geographically separate locations. A bank safe deposit box works for the public portion, while the private fragment belongs in a hidden home vault.

    Material Durability (Years)
    Titanium 50+
    Stainless Steel 30
    Archival Paper 10

    Rotate backups annually. Humidity-controlled environments prevent ink degradation on physical copies.

    Emergency Access Protocol

    Designate a trusted contact with partial information. Require multi-signature verification for fund recovery attempts.

    Legacy Planning

    Include instructions in estate documents. Probate courts increasingly recognize cryptographic assets as taxable property.

    What Is a Paper Wallet and How Does It Work?

    Store crypto keys offline by printing them directly onto a tangible medium–this handwritten or typewritten document keeps funds beyond digital reach. QR codes often encode both public and private key pairs, allowing deposits via scanning while requiring manual entry for withdrawals.

    Using this cold storage involves generating cryptographic pairs on an air-gapped device, then transferring value to the printed address. Staking your assets requires a stable connection between your physical unit and app.ledger-live-aplications. Unlike metal alternatives, these degrade over time, demanding archival paper or lamination to prevent ink smudging and brittle fracturing. Security hinges on keeping the sole copy in a fireproof safe–photocopies or digital scans defeat the purpose.

    How to Generate a Secure Paper Wallet?

    First, download a trusted offline key generator like BitAddress or WalletGenerator. Ensure your computer is disconnected from the internet to minimize exposure to potential threats.

    Create a bootable USB with a lightweight operating system, such as Tails OS, to run the generator in an isolated environment. This prevents malware from accessing your private data.

    After generating your cryptographic key pair, print it on a high-quality printer using archival-quality paper. Avoid storing the file on your device or cloud storage to eliminate digital vulnerabilities.

    For added security, laminate the printed document or store it in a waterproof and fireproof safe. This protects the credentials from physical damage over time.

    Finally, test the accessibility of your key pair by importing it into a software interface before transferring funds. This ensures the process was completed correctly without errors.

    Best Tools for Creating Paper Wallets

    BitAddress remains the most trusted offline method for generating secure cryptographic key pairs–open-source, client-side JavaScript ensures no data leaves your machine. Simply load the HTML file without internet access, move your cursor to add entropy, and print the resulting key pair for storage.

    For visually layered security, WalletGenerator’s bulk generation feature creates multiple address sets with tamper-evident folds. Users verify each segment by tearing along pre-printed perforations, exposing partial private keys only when needed–a feature unique to its design.

    Cold storage enthusiasts favor Electrum’s deterministic hierarchy–generate a master public key for receiving funds while keeping the offline private key completely isolated. Its 12-word mnemonic backup works with hardware signers, allowing transaction signing without exposing sensitive data.

    Linux users often opt for the terminal-based bitkey utility, which outputs QR-encrypted BIP38 keys directly to thermal printers. The tool writes zero temp files and overwrites memory buffers immediately after generation–critical for air-gapped systems.

    Professional institutions use Glacier Protocol’s multi-tool approach: combine an offline Raspberry Pi with Tails OS, GnuPG encryption, and mechanical dice rolls for entropy. Though complex, it withstands sophisticated attacks by compartmentalizing each generation step across separate secure environments.

    How to Safely Store and Protect Your Paper Wallet?

    Store your printed private keys in a fireproof and waterproof safe to minimize physical damage risks. Use a high-quality safe rated for at least 30 minutes of fire resistance.

    Laminate the printed document to protect it from moisture and wear. Ensure the lamination process doesn’t obscure the text or QR codes, as readability is critical.

    Avoid storing your laminated sheet in obvious locations like drawers or desks. Instead, use unconventional places, such as inside books or locked cabinets, to reduce theft risk.

    Create multiple backups and distribute them securely. Store one copy in a bank safe deposit box and another in a trusted location, ensuring redundancy in case of loss.

    Regularly check the condition of your printed document. Inspect for fading ink, smudges, or damage, and replace it immediately if any issues are detected.

    Destroy old copies securely using a cross-cut shredder to prevent unauthorized access. Never discard outdated versions without ensuring they are completely unreadable.

    How to Transfer Cryptocurrency to and from a Paper Wallet?

    To fund a printed key, scan its public address using a cryptocurrency app and send funds directly to that address. Always verify the QR code or string matches the printed information before proceeding.

    When withdrawing assets, import the private key into a software or hardware interface compatible with your cryptocurrency. Use a recognized app like Electrum for Bitcoin or MyEtherWallet for Ethereum, ensuring secure key entry without exposure to malware.

    For safety, transfer funds incrementally rather than moving the entire balance at once. This minimizes risk in case of errors or vulnerabilities during the process.

    After transferring, consider generating a new offline key for future storage to maintain security, as the previously used private key is now exposed and should no longer be trusted for long-term holding.

    Common Mistakes to Avoid When Using Paper Wallets

    Never store your backup in the same physical location as the original. A fireproof safe means nothing if both copies are inside when disaster strikes. Keep duplicates in separate secure places–preferably in different buildings.

    QR codes degrade over time. Test scans every six months, and never laminate printed copies–heat warps the alignment patterns. If storing long-term, use acid-free paper and archival ink.

    Handwriting seed phrases introduces error risks. Studies show 17% of manually recorded BIP39 words contain mistakes. Always print or use metal engraving for permanent backups.

    Ignoring address verification leads to lost funds. Before transferring large amounts, send a test transaction of ≤0.5% of the total value and confirm receipt.

    Outdated software compromises security. Generate keys only on air-gapped devices running freshly downloaded code–never reuse existing files or pre-installed tools.

    Assuming physical damage only affects paper is dangerous. Sunlight bleaches thermal prints in 9 months. Store in lightproof containers with desiccant packs to prevent moisture damage.

    FAQ:

    What is a paper wallet in cryptocurrency?

    A paper wallet is a physical document that contains a cryptocurrency public address for receiving funds and a private key for spending or transferring them. It acts as an offline method to store crypto securely, protecting it from online threats like hacking.

    Is a paper wallet safe for long-term storage?

    Paper wallets can be safe for long-term storage if created and stored correctly. However, risks include physical damage (e.g., fire, water) or loss. For added security, laminate the paper, keep multiple copies in secure locations, and avoid exposing the private key digitally.

    Can you send partial funds from a paper wallet?

    No, paper wallets are designed for one-time or full withdrawals due to how private keys work. To spend part of the balance, you must transfer the entire amount to a software wallet first, then send the desired portion to another address.

    What is a paper wallet and how does it work?

    A paper wallet is a physical document that contains a cryptocurrency address and its corresponding private key, usually printed in the form of QR codes. It functions as a cold storage method, meaning it’s entirely offline and not connected to the internet, which reduces the risk of hacking. To use it, you can scan the QR codes with a wallet app to access your funds or transfer cryptocurrency to the address printed on the paper. It’s a simple way to store crypto securely, but it requires careful handling to avoid loss or damage to the paper.


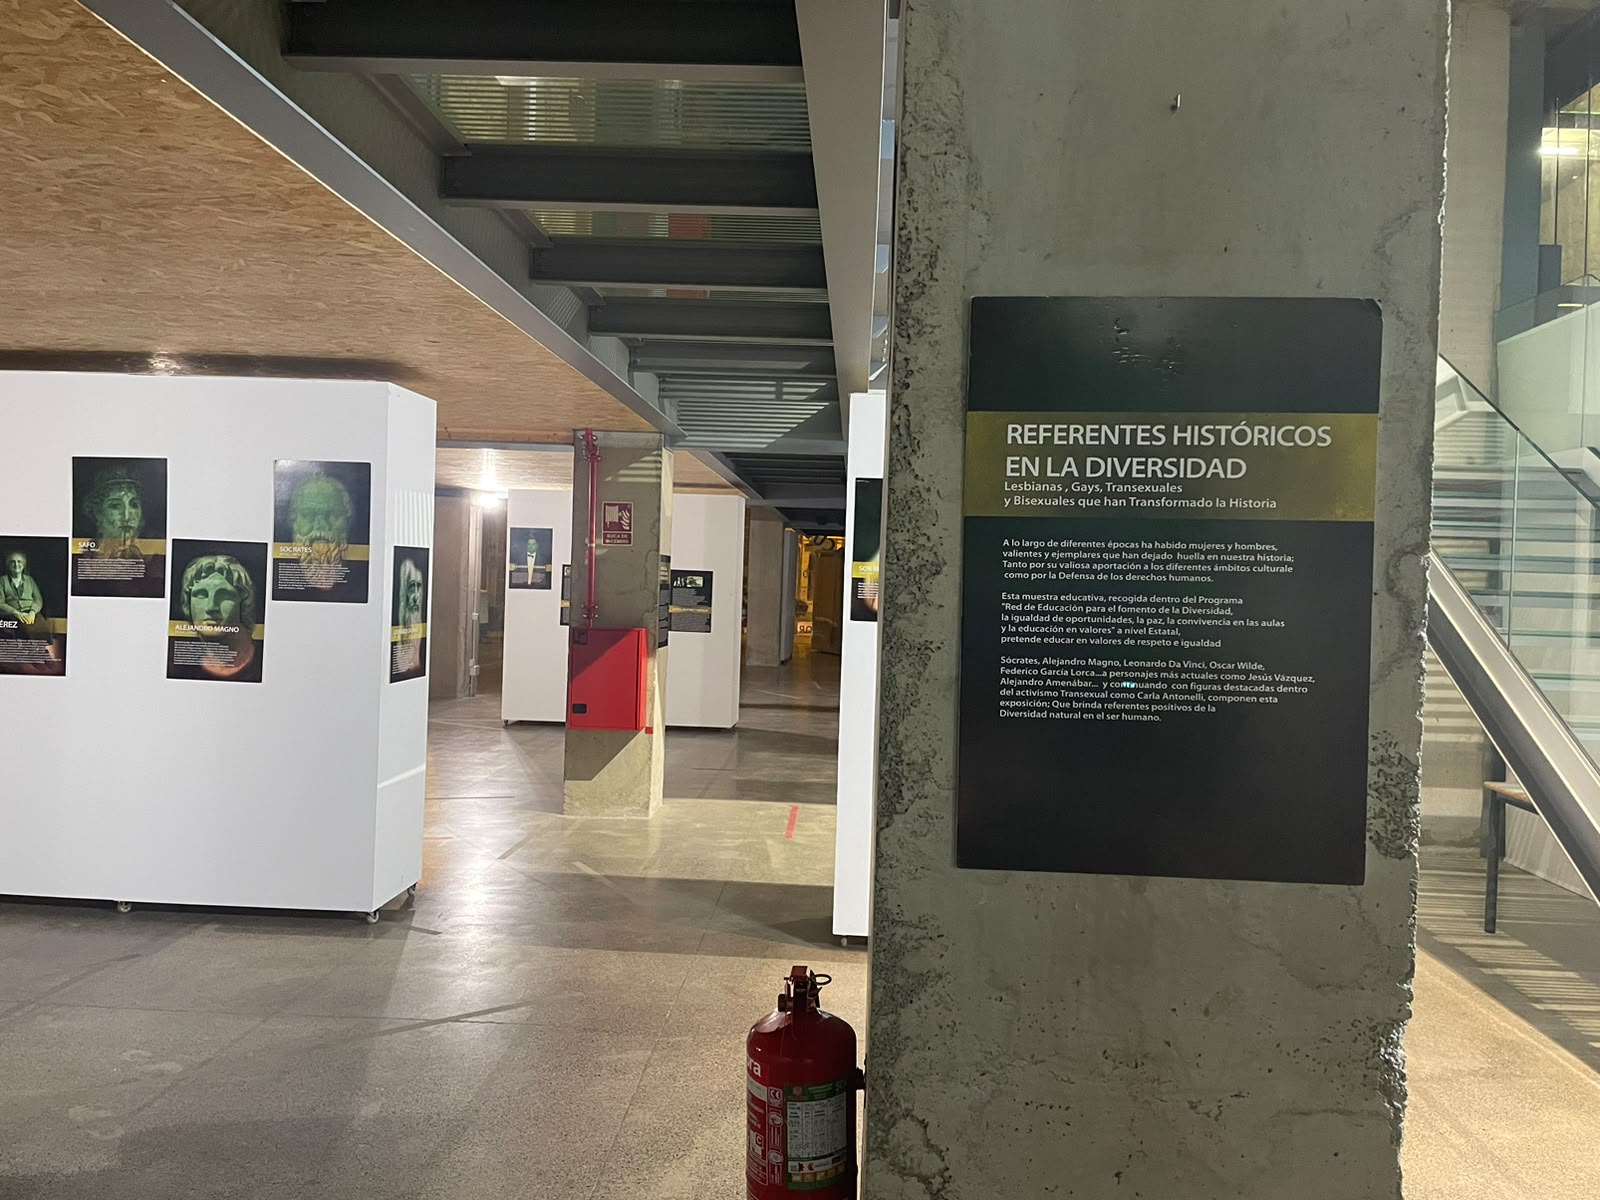
  • GALACTYCO expone en el CIM una muestra de referentes históricos en la diversidad desde Sócrates a la actualidad

    Hasta el 30 de septiembre se podrá visitar esta exposición gracias a la colaboración del servicio de Igualdad y Diversidad y el Consejo de Estudiantes de la UPCT

    Cartagena (10/9/26).La asociación de gays, lesbianas, trans y bisexuales activistas de Cartagena y Comarca ‘Colectivo GALACTYCO’ ha inaugurado hoy en la sala de exposiciones del campus del antiguo Cuartel de Instrucción de Marinería una muestra sobre referentes históricos en la diversidad, con unos paneles de una serie de personajes conocidos, homosexuales, transexuales o bisexuales, de distintas épocas, que van desde Sócrates hasta personalidades de la actualidad.

    La exposición se podrá visitar hasta el 30 de septiembre y está organizada de la mano del Servicio de Igualdad y Diversidad y el Consejo de Estudiantes de la Universidad Politécnica de Cartagena.

    “El objetivo de la exposición es dar a conocer referentes positivos, desde Sócrates a personalidades actuales como Jesús Vázquez, para que los jóvenes homosexuales, bisexuales o transexuales no se sientan solos y para combatir, desde el conocimiento, la homofobia, la bifobia o la transfobia que continúan existiendo, como lo prueban los casos de acoso escolar que siguen padeciendo los chavales con estas tendencias sexuales», según ha puesto de manifiesto el presidente del colectivo Galactyco, Miguel Ángel Casanova.